

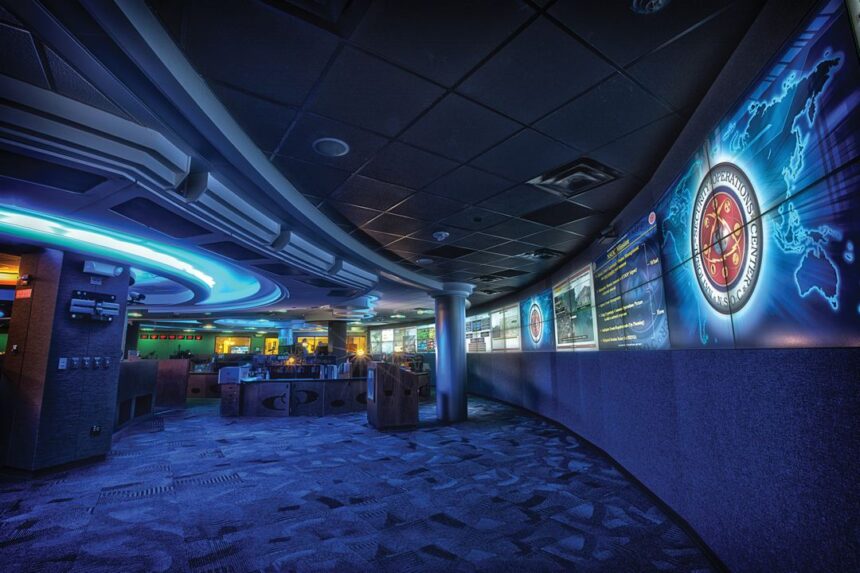
Cyber security operations centres are adopting faster detection tools as attacks arrive in shorter bursts and target a wider range of organisations. Modern platforms combine network traffic, login records and device alerts into a single view, helping analysts spot suspicious patterns that once took hours to assemble manually. Automated triage now handles routine warnings, reserving human attention for incidents that show genuine signs of intrusion. Leaders say speed matters because attackers can move from an initial breach to data theft very quickly. Specialists following cyber security operations say smaller firms are increasingly buying shared monitoring services rather than building their own centres. That model gives them overnight coverage and access to experienced analysts at a predictable cost. Ransomware remains the most feared threat, but credential theft and supplier compromise are rising concerns. Centres are practising response drills with legal, communications and executive teams so decisions are rehearsed before a real crisis. Regular patching and multi factor authentication still prevent many incidents entirely, a reminder that advanced tools work best on strong basic foundations.
What the Evidence Shows
Analyst recruitment remains difficult, with experienced staff in high demand across finance, health and government. Centres are responding with apprenticeships and clearer progression routes for junior analysts. Automation helps retention by removing repetitive alert checking, but leaders warn against trusting software verdicts without human review. False positives can hide genuine attacks in a flood of notifications, so tuning systems to each organisation environment is continuous work. Threat intelligence sharing between sectors has improved, allowing a warning discovered by one centre to protect many others quickly. Attackers are also using artificial intelligence to craft convincing phishing messages, raising the value of staff training and reporting culture. When employees report suspicious emails early, response teams gain precious time. Budgets are under pressure, yet boards increasingly view monitoring as essential insurance. The centres that perform best combine technology, practised teamwork and honest post incident reviews that turn every scare into a lesson. Reporting and analysis from sources such as IEEE Spectrum track the same developments, and specialists following cyber security operations say the direction is now consistent across independent lines of evidence.
The Wider Context
Adoption of cyber security operations follows a familiar pattern with an unfamiliar speed. Early users tolerate rough edges in exchange for advantage, mainstream users arrive when the tool disappears into existing workflows, and the market consolidates around whoever made that transition feel effortless. Vendors are racing less on raw performance now than on integration, support and trust.
What Happens Next
The realistic forecast for cyber security operations is steady integration rather than sudden replacement: embedded in products people already use, improving in increments, and regulated in proportion to its reach. The companies and institutions that plan on that basis, training staff and redesigning processes instead of chasing launches, are the ones the adoption data tends to vindicate. You can follow related developments in our coverage of technology.
It is also worth remembering how quickly the picture in this area has changed before. Positions that looked settled a few years ago have been revised as new data arrived, and the same humility is appropriate now. The strongest coverage of this subject, and the most useful advice, tends to come from sources that update their views openly when the facts move, rather than defending an earlier position long after it has stopped fitting the evidence available.